

Keeper launches Freshservice workflow for access requests
Fri, 16th Oct 2026 (Today)
Keeper Security has launched a Freshservice Workflow integration for vault and privileged access requests, linking Keeper approval tasks to the Freshservice tickets used by IT and security teams.
The workflow is designed to let agents handle access requests from a Keeper Vault tab within a Freshservice ticket, rather than switching between separate systems. Staff can search the Keeper vault, set permissions, and approve or deny requests from that interface, according to Keeper.
The integration also covers Endpoint Privilege Manager and Cloud SSO device approvals. When paired with Keeper's ITSM for Freshservice app, those functions give administrators a single ticketing interface for incident-led requests and routine approval work.
Audit trail
Access approvals are often created in a helpdesk platform but completed elsewhere, which can cause delays and leave parts of the process outside the formal audit record. Keeper's Freshservice integration is intended to keep those decisions within the ticketing workflow already used by support and security teams.
Under the setup, each action runs through a customer-hosted Keeper Commander ServiceMode endpoint. This, Keeper said, preserves its zero-knowledge encryption model and means credentials are not stored in Freshservice.
That architecture is central to the product's pitch. Keeper argues that keeping approval steps in a governed system reduces the use of email or chat for access decisions, where records may be incomplete or harder to audit.
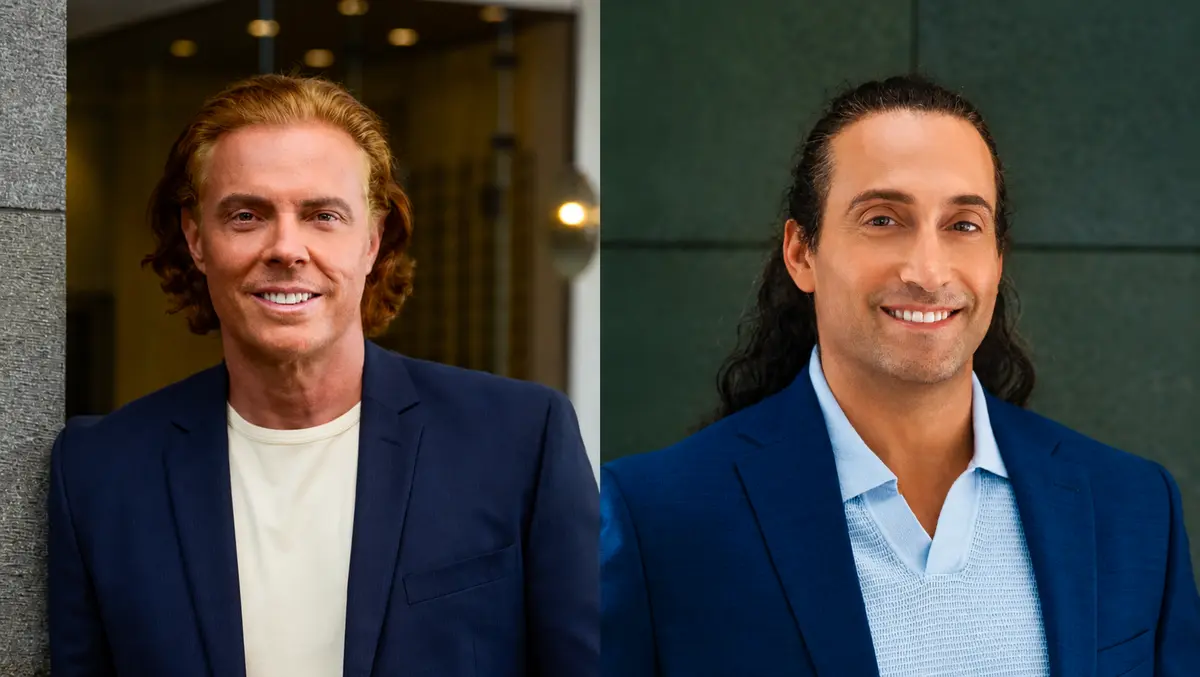
"The cryptographic boundary cannot move outside Keeper," said Craig Lurey, Chief Technology Officer and Co-founder of Keeper Security.
"This integration processes every approval through Commander ServiceMode on infrastructure owned and controlled by the customer, so the attack surface doesn't expand when you wire Freshservice into your approval workflow. Freshservice is the interface for the request, never the place where secrets are stored," Lurey said.
Access controls
The launch reflects a broader focus across corporate IT on tightening controls around who can access sensitive systems and when. Privileged access management tools are increasingly being linked with service management platforms so approvals, policy enforcement, and record-keeping sit in one operational flow.
Keeper said the workflow is intended to reduce the handoffs that can slow decisions after an employee raises a service request. In a typical process, an agent may need to leave the ticket, log in to another system, find the relevant record or folder, grant access manually, and then report back in the helpdesk tool.
By allowing those steps to happen within the ticket sidebar, the integration is intended to remove a common bottleneck in access administration. The goal is to reduce delays while maintaining oversight of who requested access, who approved it, and where the decision was recorded.
Keeper also linked the move to growing demand for stronger identity governance as organisations manage access requests from both employees and systems. That includes requests related to devices and cloud sign-on, as well as access to items stored in a vault.
"Every access request is an identity decision, and the further those decisions drift from a governed system, the weaker the audit trail becomes," said Darren Guccione, Chief Executive Officer and Co-founder of Keeper Security.
"Integrating Keeper into Freshservice keeps approval decisions inside a ticketing system that security teams already trust, which means zero standing privilege and full audit control stay intact. This becomes increasingly important in the agentic era, as access requests multiply across both human and machine identities," Guccione said.
The Freshservice Workflow app is available through the Freshworks marketplace for organisations with an active Keeper Commander deployment, according to Keeper.