Threat intelligence stories
Threats are now spanning identities, cloud and software supply chains, with AI speeding attacks and complicating defence, Microsoft says.
The combined group would give Microsoft customers broader AI-led threat detection and response, with no deal value disclosed.
Security teams can now test whether their tools spot attacks, after UltraViolet Cyber said Equinox can map gaps in under 30 minutes.
The deal gives security teams a widely used AI testing tool with on-premises controls, as vendors race to speed up offensive defence.
Many firms are still exposed to faster AI-driven attacks, with Logicalis finding 64 per cent lack mature round-the-clock security operations.
Security teams could cut investigation time from hours to minutes as Exabeam adds AI tools for triage, reporting and local deployment.
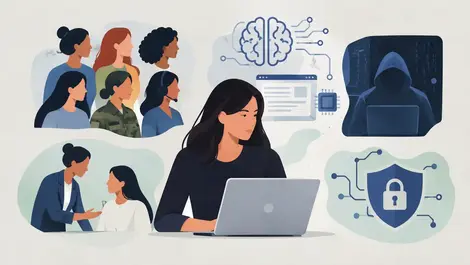
The report says threat intelligence teams could benefit from wider hiring pools as women bring skills from fields from marketing to the military.
MacOS users can now be covered by Hexnode's XDR as the update aims to cut alert overload and speed up threat response for IT teams.
Smaller firms across Australia and New Zealand face rising cyber losses as vendors warn that AI, cloud sprawl and quantum risks are widening exposure.
Affected organisations may still face unauthorised access after patching, as researchers found attackers using scripts and reverse shells on NetScaler devices.
Data theft is now driving ransom demands, with average payments rising and attackers increasingly targeting senior staff at exposed companies.
Manufacturers, hospitals and service firms face escalating extortion threats as organised crime drives most attacks across Australasia.
The merger is set to give Microsoft customers broader AI-led threat detection, response and recovery support across North America, the UK and DACH.
Fresh capital will fund Hackuity's push into Europe and Asia as firms struggle to prioritise a swelling backlog of vulnerabilities.
Enterprises face new controls as the partnership aims to stop autonomous AI agents from accessing data, credentials and tools unchecked.
Boards are being urged to beef up defences as AI tools may soon help criminals automate attacks and target New Zealand organisations more precisely.
Security teams can now isolate affected Macs as Hexnode extends XDR threat detection and response beyond Windows with new remediation tools.
Security teams can now triage Mac endpoints faster as Hexnode adds AI-led alert ranking, threat feeds and automated remediation to XDR.
Security teams can now isolate affected Macs as Hexnode extends XDR with auto remediation, threat intelligence and severity-based alert ranking.
Security teams can now verify which reported weaknesses are actually exploitable in their own environments before spending time on false alarms.