Remote Access stories
Growing IT-OT convergence is sharpening demand for tools that can reduce disruption to factories, transport networks and critical infrastructure.
Business systems supporting factories, logistics and utilities remain vulnerable, with Australia accounting for 20 of 23 industrial ransomware incidents in the region.
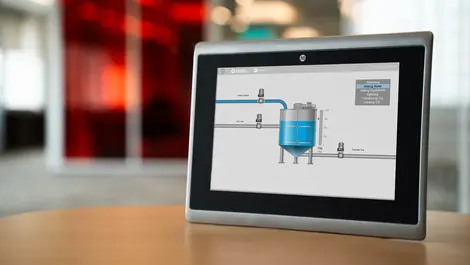
It could cut downtime and revalidation costs for factories upgrading ageing HMI systems by letting them reuse existing FactoryTalk View ME applications.
Industrial firms bore the brunt as ransomware incidents climbed 23% in the third quarter, with North America also hit hard.
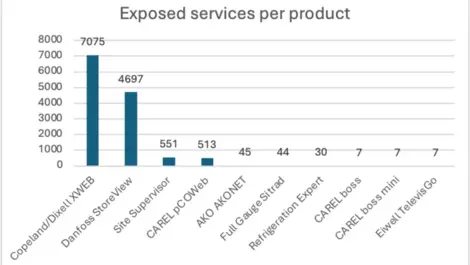
Researchers found nearly 13,000 exposed refrigeration services in 99 countries, widening fears that remote access could disrupt food, medicine and storage.
Industrial operators can now buy continuous monitoring and response support as Integrity360 expands beyond one-off OT assessments and consulting.
Systems that polled AOMEI's update servers at the wrong moment could have pulled malicious files in the brief April-to-July tampering window.
Researchers say the scheme has run since 2017, exposing users to fake Microsoft alerts and remote access theft through legitimate hosting tools.
IT teams are under growing pressure as attackers use AI to exploit vulnerabilities faster, prompting Splashtop to expand its security tools.
Affected organisations face credential theft and network intrusion risks after a zero-day in BeyondTrust Remote Support was abused before disclosure.
Organisations can now limit contractors and staff to approved machines only, avoiding wider network exposure and reducing reliance on VPNs.
Developers may have been steered towards malicious code as at least 88 public GitHub repositories linked to a malware cluster surfaced in AI recommendations.
More than two-thirds of UK organisations have slowed AI and edge rollouts, while better network resilience is linked to GBP £3.2 million lower outage costs.
More remote access and distributed assets are leaving power firms exposed to credential theft, with compromised accounts implicated in 19 per cent of incidents.
More connected water networks are widening the risk of stolen logins disrupting treatment, service delivery and public confidence.
The update lets administrators investigate faults on Windows and macOS devices without taking over users' screens, reducing disruption during support work.
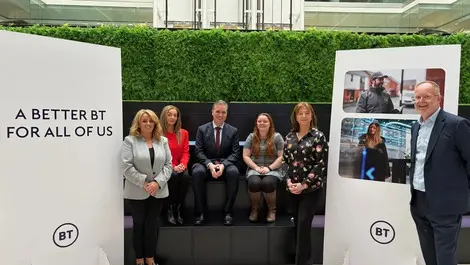
More than 5,000 Scottish hospitals, schools and councils now have upgraded connectivity after BT finished a £350 million network programme early.
Thousands of households were unknowingly used as residential proxies after preloaded malware infected Android TV boxes in 34,206 Australian devices.
Industrial operators can now outsource continuous protection as the new service set aims to reduce cyber risk without disrupting production.
Stolen information is now the main pressure point in cyber intrusions, with exfiltration appearing in 83 per cent of cases investigated in the third quarter.