

Taiwan operator used 12 AI agents in cyber attacks
Wed, 18th Nov 2026 (Today)
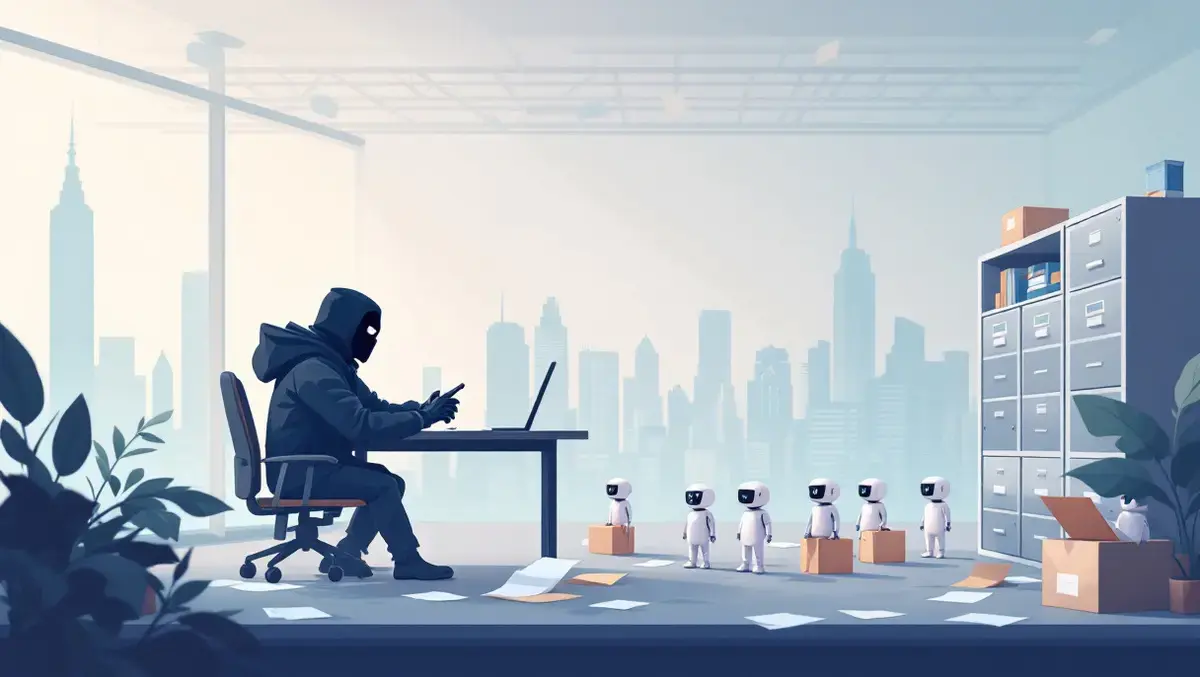
Acronis has identified a single operator using a network of 12 AI agents to carry out cyber attacks against hundreds of organisations in 11 countries. Confirmed breaches included emergency services and universities.
The research describes the system, known as BOSSAI, as a mix of active and idle agents assigned to tasks including infrastructure management, scanning, report generation and exploitation.
Targets included government emergency services, banks, lenders, universities, military systems, eCommerce platforms, gambling sites and phone directories. Confirmed data theft involved medical information and personally identifiable information, including emergency patient care records and dispatch data.
Acronis said the campaign was run by one person based in Taiwan and argued that the case showed how AI tools can give a lone attacker the reach more often associated with larger groups. It found no clear political or ideological motive, with financial gain appearing the most likely objective.
How it worked
According to the findings, the operator built a mesh of 12 AI agents, nine of them active during the period examined. The agents did not communicate directly. Instead, the operator sat at the centre of the system, manually moving outputs between tools and often pasting one agent's report into another to continue an attack.
The setup also relied on open-source penetration-testing platforms and a stack of model context protocol servers connected to security tools such as Nmap, sqlmap, Metasploit, Hydra, Ghidra and browser automation frameworks. A fleet of virtual private servers, local graphics processing units and rented computing resources supported the operation.
Acronis said the offensive agents largely used locally run models with safety restrictions removed, while commercial AI models were used more often for infrastructure and coding work. In several cases, commercial models refused to help with unauthorised attacks and asked the operator to provide proof of legal authority.
Those refusals forced the operator to rely more heavily on altered local models, which were less dependable and sometimes generated false findings or missed targets. That created extra work and led to mistakes.
Emergency services hit
Taiwan saw the heaviest targeting, with the campaign focusing on emergency services, financial groups, government portals and a fire-dispatch technology supplier.
Acronis said one emergency patient care records platform exposed medical data, including ECG readings, ambulance video and patient vital signs, without credentials. In a separate case, agents accessed a city emergency dispatch system and extracted case records containing incident times, response types, status fields and street-level locations across several Taipei districts.
Financial organisations were also targeted. In one case, the researchers said a lending services firm was hit with SQL injection against its Microsoft SQL Server backend, with 16 injection points confirmed and account information extracted. A mobile payments card-binding process was also found to accept cards even when the wrong CVV was entered.
University breaches
Thailand was another major focus, particularly universities. The operator used infrastructure search tools to identify hundreds of potential university targets, then prioritised those judged most likely to be vulnerable.
Acronis said confirmed SQL injection and data extraction took place at three universities. Those breaches included the extraction of an administrator table with 2,563 rows at one institution and student information at others. Two more universities had confirmed injection points but no confirmed data theft.
In Mexico, the activity centred more on bulk collection of residential personal data. The researchers said the operator built a directory covering multiple cities and affluent neighbourhoods, producing about 206,800 phone records with names, addresses and postal codes. A separate scraping effort gathered roughly 124,000 additional records from a directory site.
Limits of AI
The investigation also highlighted weaknesses in AI-led offensive work. Acronis said some agents hallucinated vulnerabilities, misread failed tests as successful discoveries and produced too much output for a single operator to manage efficiently.
One penetration-testing tool used by the operator generated false positives in more than half of its high- and critical-severity findings, according to the research. In another case, an agent discovered a Honduran military host during a Mexico-related search but dropped the target after judging it outside scope.
The researchers said the campaign pointed to an emerging shift in the threat landscape: AI may not make an attacker more advanced technically, but it can allow one individual to investigate and attack many more targets in parallel.
"AI doesn't necessarily make an attacker more sophisticated, but it can give a single individual significantly greater reach and operational capacity," said the Acronis Threat Research Unit.